Microsoft Azure Alerts Integration Guide
Microsoft Azure is one of the most popular cloud hosting platforms. It allows clients to set up alerting monitors to get notified about unusual system usage, performance and other related metrics. TaskCall integrates with Microsoft Azure and ingests these alerts and dispatches them to the correct on-call responders persistently through various channels so that the incidents raising the alerts can be addressed in real time without causing any damage to their operations.
Pointers
- The integration is between a TaskCall service and Microsoft Azure.
- Incidents will automatically resolve in TaskCall when metrics fall back within the normal threshold.
- This integration only receives alerts in TaskCall from Microsoft Azure.
In TaskCall
- Go to Configurations > Integrations and click New Integration.
- Select the Microsoft Azure Alerts integration.
- Give the integration a name and configure how incidents will be created. Only the Default Service field is required. The rest are optional.
- Incidents (Optional)
- TaskCall automatically maps incoming payloads with internal attributes to create incidents. However, this can be customized in the Incidents tab. Constant values can be included alongside placeholders to dictate which attributes should map to the Incident Title, Description, Tags, Snapshots and Vendor URL. To insert a placeholder use double curly braces.
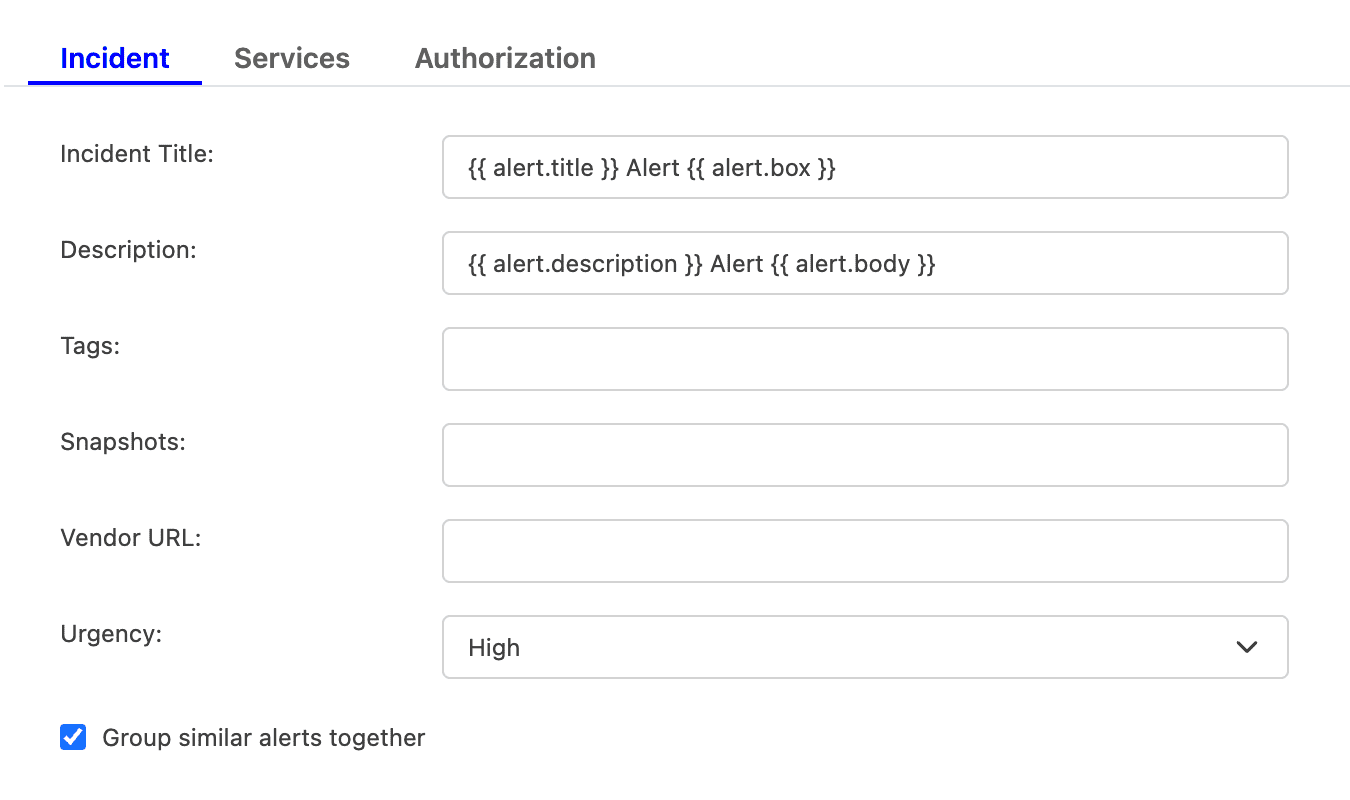
For example, if you enter {{ alert.title }} in the Incident Title field, TaskCall will look for an attribute called "title" nested inside another attribute called "alert" in the incoming payload. If the nested attribute exists, its corresponding value will be pulled from the payload and inserted. If the nested attribute does not resolve successfully, TaskCall will fall back to the default mapping.
If you are unsure, please leave the fields empty. TaskCall will use the default mapping to create the incident for you. - Select the Urgency level the incident should be created at.
- Select the option to Group similar alerts together if you would like follow up triggers from the same alert source to be grouped into the same incident. If you leave this option unchecked, then a new incident will be created for every trigger. (This behavior is specific to new triggers; not updates to an alert.)
- Click Next to move on to the Services tab.
- TaskCall automatically maps incoming payloads with internal attributes to create incidents. However, this can be customized in the Incidents tab. Constant values can be included alongside placeholders to dictate which attributes should map to the Incident Title, Description, Tags, Snapshots and Vendor URL. To insert a placeholder use double curly braces.
- Services (Required)
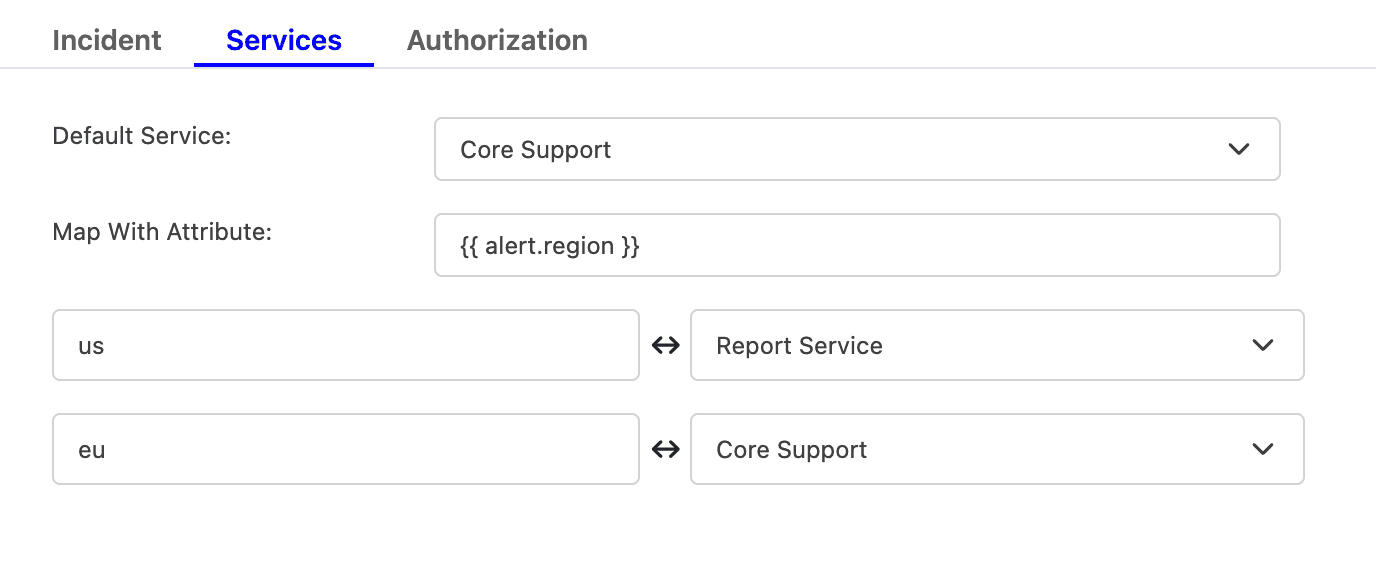
- Select the Default Service incidents should be sent to. To route incidents to different services instead, set Map With Attribute to the attribute to route by using a placeholder. Then, map each value it can take to the service that should receive it.
For example, to route by a region attribute sent in the payload, set Map With Attribute to {{ region }}, then map US to one service and EU to another, and so on.
- Click Next to move on to the Authorization tab.
- Select the Default Service incidents should be sent to. To route incidents to different services instead, set Map With Attribute to the attribute to route by using a placeholder. Then, map each value it can take to the service that should receive it.
- Authorization (Optional)
- The Authorization tab allows a Bearer Token and an IP Allowlist be added if you would like to restrict who is able to send alerts to this integration. If you are unsure, this can be skipped.
- Once done, click Save.
- Copy the Integration Url that is issued for the integration. This will be used to set up the notification in Microsoft Azure Alerts.
In Microsoft Azure
- For the Microsoft Azure Alerts integration we will first create an action to send alerts to TaskCall and then alerts that will trigger the action.
- Once you are logged into your Microsoft Azure Portal, from the portal menu, go to Monitor > Alerts > Manage Actions.
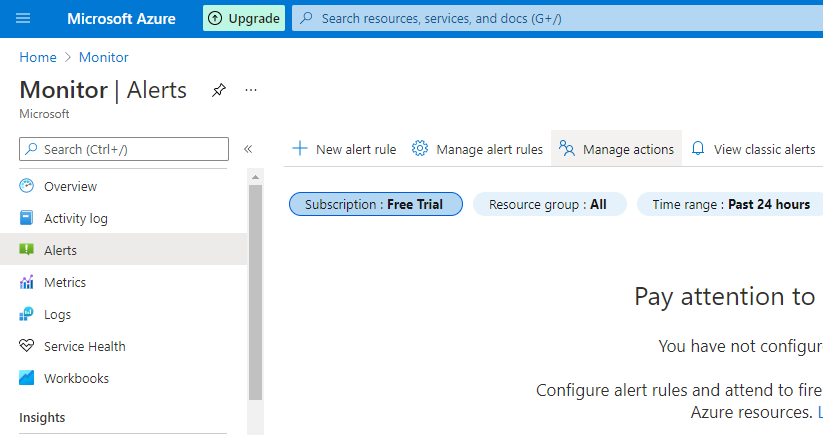
- Click New Action Group .
- Under the Basics tab select your subscription, select your resource group and give the action group a name.
- Go to the Action tab. Select Webhook as the Action Type. Give the webhook a name. In the URI section on the form that pops up on the left, paste the Integration Url you copied over from TaskCall. Enable the common alert schema.
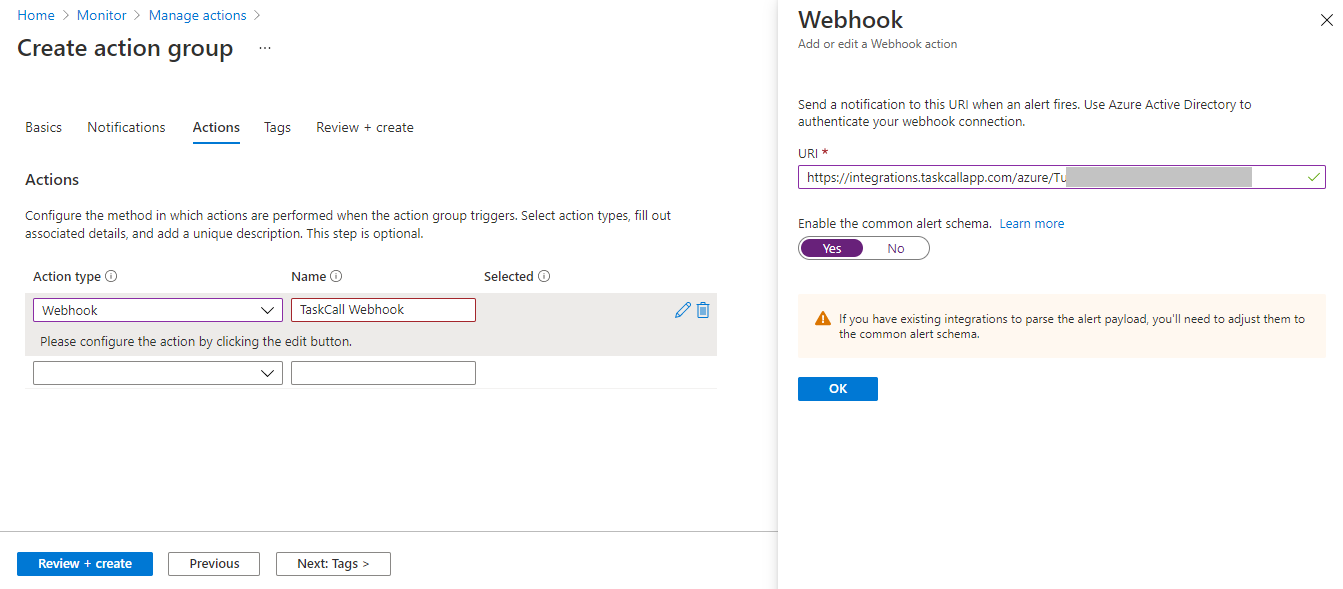
- Click OK on the pop up to set the webhook url.
- Go to the Review + create tab. Click Create.
- We are done setting up the endpoint that will allow TaskCall to receive alerts from Microsoft Azure. Now we will create an alert to test it with.
- Go to Monitor > Alerts > New alert rule.
- Select the resource you want to trigger the alert on. Set the conditions (metrics and threshold) the alert should trigger on. In the Actions section, select the action group you created earlier.
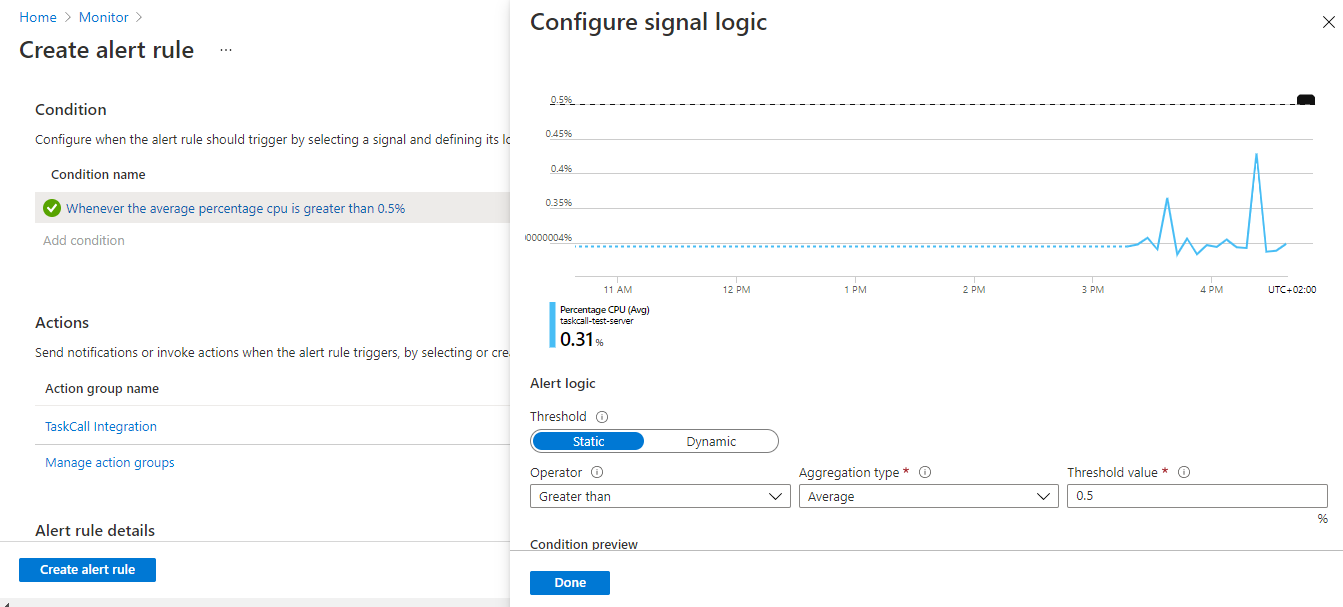
- In the Alert rule details section give the alert a name, a description and ensure that the checkboxes for both Enable alert rule upon creation and Automatically resolve alerts are checked.
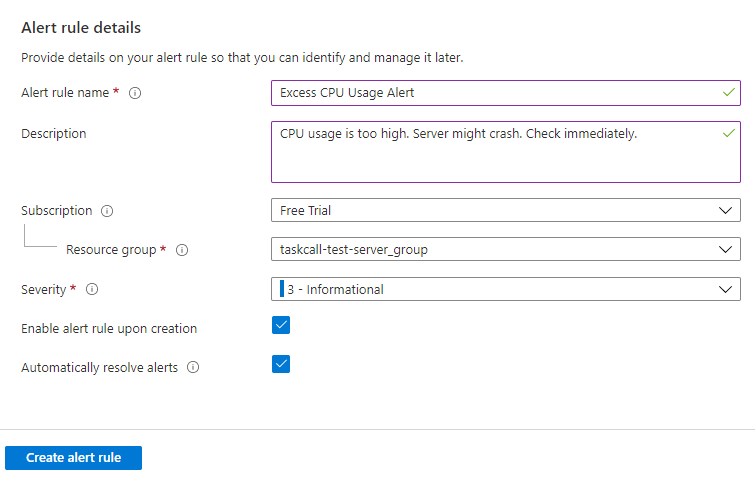
- Click Create alert rule.
- Done! Now whenever your monitoring metrics will go outside the set threshold, incidents will be triggered on TaskCall. The incidents will also automatically resolve when the metrics come back within the acceptable range.